Welcome back to our Enterprise Network Specialist training series! If you have followed along with our journey through log monitoring and Zero Trust models, you already know how vital security is. However, before we monitor traffic, we must build our first line of defense: Network Hardening and Firewall Architecture.
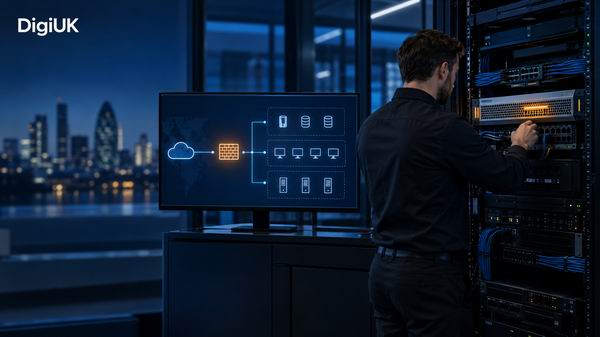
Think of a corporate network like a modern house. You would never leave every window wide open and the front door unlocked. Instead, you lock down every router and switch. Furthermore, firewalls act as smart security gates that inspect visitors. Let us break down how professional engineers build these boundaries.
1. Why Network Hardening and Firewalls Matter
As cyber threats grow, default settings on network hardware invite attackers. Specifically, vendors ship routers with standard passwords and open ports for convenience. Therefore, engineers must harden them.
-
Reducing Attack Surfaces: Hardening involves closing unused ports. Consequently, attackers find zero easy entry points.
-
Stateful Packet Inspection (SPI): Modern firewalls track connection context. Thus, they ensure only legitimate returning traffic passes through.
-
Defense in Depth: Firewalls form the structural perimeter. Meanwhile, internal VLANs slow down lateral movement if a breach occurs.
2. Core Concepts of Access Control and Stateful Filtering
Managing traffic effectively requires strict rule enforcement using Access Control Lists (ACLs) and stateful rule tables.
Important Note: Never leave remote management protocols like Telnet enabled. Always enforce encrypted SSH or HTTPS connections for administrative access.
Key Architectural Principles:
-
Implicit Deny: This is the golden rule of firewall design. If traffic lacks explicit permission, the system blocks it automatically.
-
Zone-Based Segmentation: Engineers separate networks into distinct zones. For example, a DMZ holds public web servers, while an internal LAN serves employees.
-
State Tracking: Firewalls maintain dynamic state tables. As a result, they recognize whether a packet belongs to an authorized connection.
3. Step-by-Step Hands-On Lab: Checking Firewall Rules and Network Interfaces
Let us review a practical task you can run in your lab to inspect packet filtering rules:
# Inspect current iptables firewall rules and filter chains on a test node
iptables -L -v -n

# Check active network interface bindings and routing tables
ip route show
-
Step 1: Open your lab terminal and run the
iptablescommand. Consequently, you will review how packet filtering rules are structured. -
Step 2: Use Wireshark to capture gateway traffic. Thus, you verify that unwanted packets drop correctly.
-
Step 3: Document your firewall rule ordering. Specifically, ensure that the implicit deny rule sits securely at the bottom of the chain.
4. Best Practices for Enterprise Firewall Management
Maintaining a secure firewall architecture requires ongoing maintenance, regular audits, and strict change control:
| Security Focus | Practical Description | Recommended Action Item |
| Rule Hygiene | Firewalls accumulate dead rules over time, creating blind spots. | Conduct quarterly firewall rule audits to remove redundant access rules. |
| Firmware Upgrades | Gateway operating systems contain vulnerabilities that attackers target. | Establish a routine schedule for applying security patches to all hardware gateways. |
| Backup Configurations | Hardware failure can instantly bring down a corporate network. | Automate daily encrypted backups of all firewall configuration files. |
-
Change Control Procedures: Never make ad-hoc rule changes on production firewalls without prior testing.
-
Log Analysis: Routinely review firewall drop logs. As a result, you spot external reconnaissance attempts early.
External Resources & Further Reading
-
Explore infrastructure hardening guidelines via the NIST Computer Security Resource Center.
-
Review enterprise gateway design standards at the Internet Engineering Task Force (IETF).
-
Catch up on our previous training module on Network Monitoring, SIEM, and Security Operations.