The Digital X-Ray: Understanding Vulnerability Assessment in Ethical Hacking
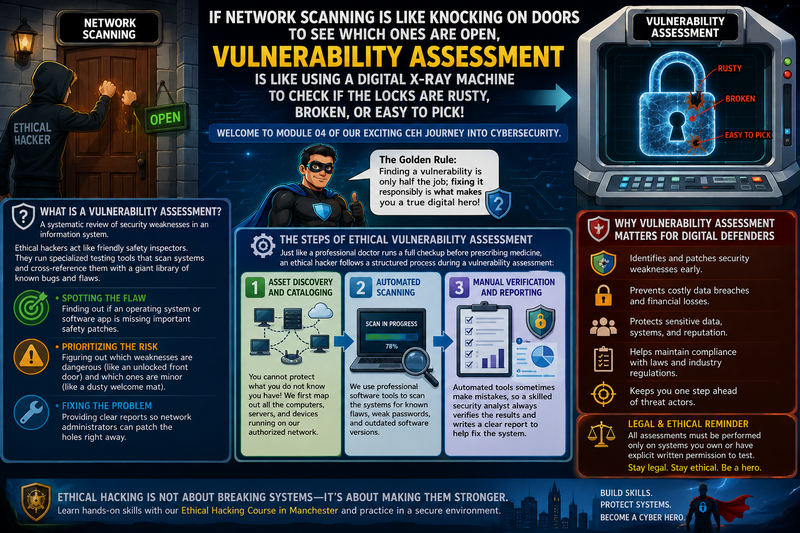
If network scanning is like knocking on doors to see which ones are open, Vulnerability Assessment is like using a digital X-ray machine to check if the locks are rusty, broken, or easy to pick! Welcome to Module 04 of our exciting CEH journey into cybersecurity. Today, we are going to learn how cyber superheroes […]
What is Network Scanning?
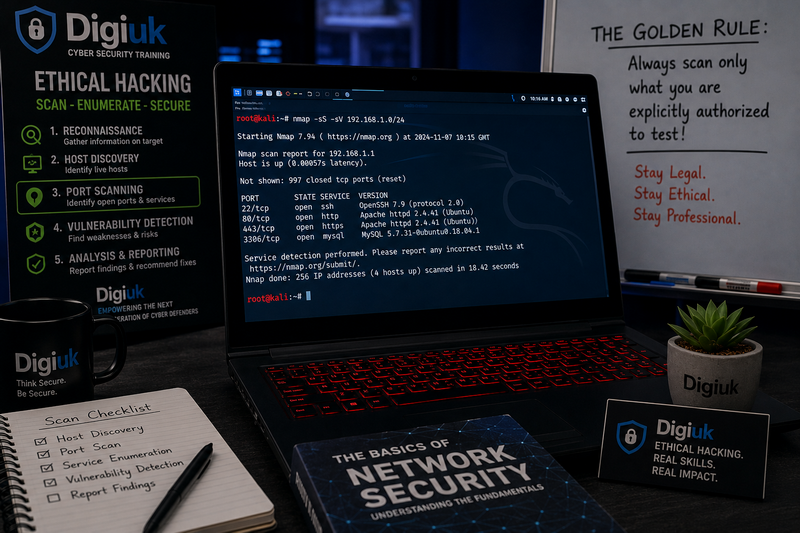
Once a digital detective has a list of IP addresses from their reconnaissance phase, they need to know what those computers are actually doing. Network Scanning allows us to identify live systems and discover open ports. Every computer has thousands of “digital doors” called ports. Some are meant to be open, like a web server […]
The Digital Spyglass: How Ethical Hackers Gather Clues Safely Online
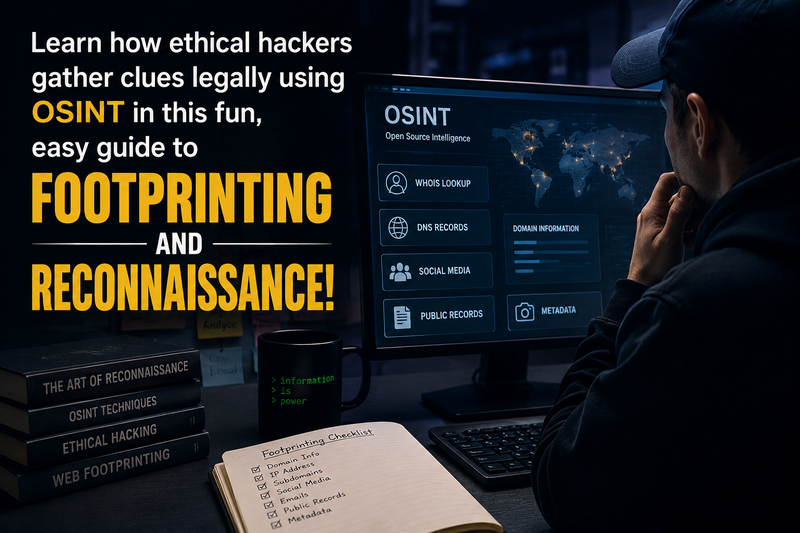
Have you ever played hide-and-seek and looked for clues—like a rustling curtain or a pair of shoes peeking out from behind a door? In the world of cybersecurity, digital detectives do the exact same thing before they ever touch a keyboard! This sneaky (but totally legal!) clue-gathering is called Footprinting and Reconnaissance. Today, we are […]
The Digital Detective’s Code: Understanding the UK Computer Misuse Act 1990
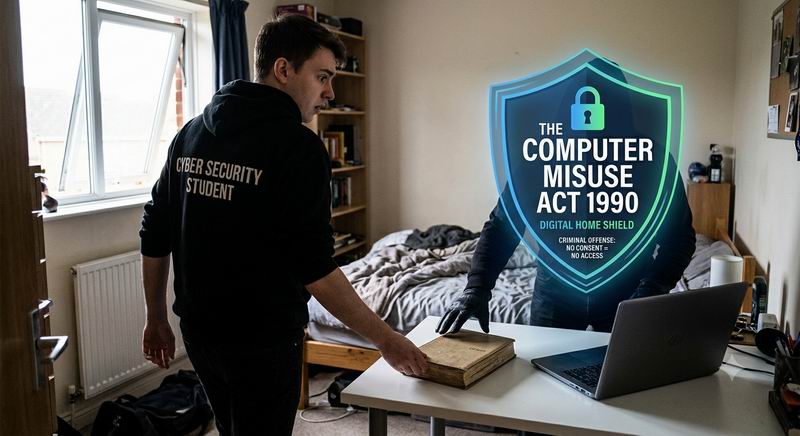
Have you ever wondered how digital superheroes keep the internet safe? Just like real-world police officers, ethical hackers must follow strict rules to ensure they are always doing the right thing. Today, we are going to explore the ultimate rulebook for computers in the United Kingdom: The Computer Misuse Act 1990! What is the Computer […]
Ethical Hacker Methodology Steps: The Fun Guide to System Hacking
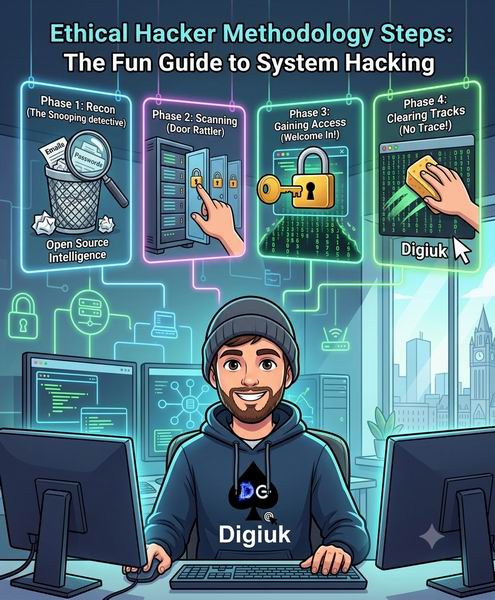
Trying to memorize the official ethical hacker methodology steps can sometimes feel like reading a microwave instruction manual. But if you want a great offensive security framework overview that actually sticks in your brain, you need to think of a hacker less like a movie spy and more like a nosy neighbor trying to figure […]
Supply Chain Safety: Mastering ISO 27001 Supplier Relationships
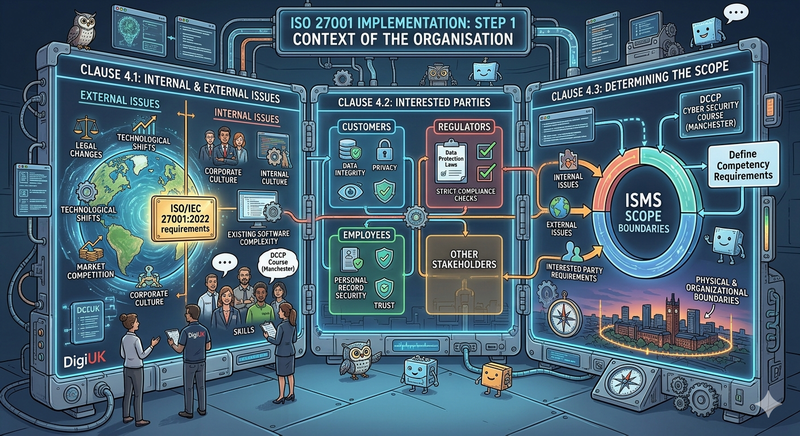
Even if your internal networks use ironclad defenses, your data can still face exposure through external partners. Therefore, you must manage the third-party platforms, contractors, and cloud vendors that interact with your systems. ISO 27001 Supplier Relationships (detailed in Annex A.5.19 through A.5.23) provide the ultimate roadmap for third-party risk management. By setting clear security […]
Digital Defense Basics: Mastering ISO 27001 Technological Controls
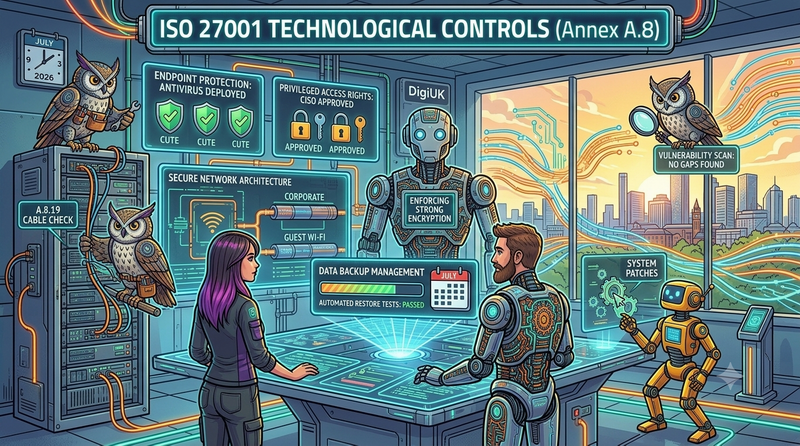
Once you secure your team and lock your office doors, you must build your ultimate digital defenses. Therefore, we must dive directly into the largest technical section of the standard. ISO 27001 Technological Controls (found in Annex A.8) contain the actual computer configurations that block hackers. By setting up these rules correctly, you create an […]
Locking Down the Fort: Mastering ISO 27001 Physical Controls
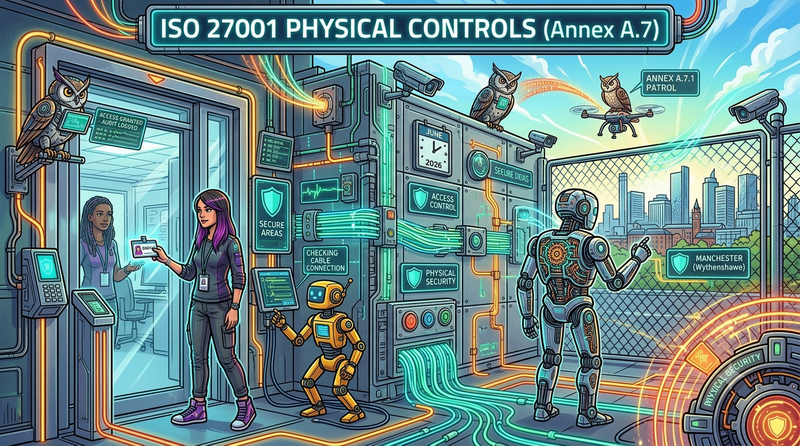
Digital encryption cannot protect your business if an intruder walks straight into your office. Therefore, true data safety requires physical barriers alongside your digital firewalls. Consequently, ISO 27001 Physical Controls (Annex A.7) are absolutely vital for modern business compliance. These controls provide a clear blueprint to build multiple layers of protection around your building. As […]